


NexappOS: one secure operating system, from the edge to the cloud
One operating system on every Nexapp router and edge, on your own servers and hypervisors, in public cloud and in the data centre. Post-quantum signed, so you can grow from one router to full SASE on one platform.
- 75,000+
- Devices in production
- Since 2014
- Developed and maintained in Pune
- 1 firmware
- From ATM router to SD-WAN edge
- Post-quantum
- Signed images, ML-KEM tunnels
SD-WAN, routing, security and VPN in one operating system
NexappOS is the operating system behind every Nexapp router, edge and virtual edge. On Nexapp hardware it comes installed, and we maintain it everywhere it runs.
FlowEdge MultiWAN
Any-port WAN with link backup, switch and load balance by policy; dual-SIM arbitration by signal, latency or data usage.
SD-WAN Fabric
Encrypted bonding overlay with SLA health, SD-WAN rules, application-aware routing and mesh topologies.
Routing and QoS
BGP, OSPF, RIP, PIM and VRF, static and policy routing, Performance SLA and Adaptive QoS.
High availability
Active and standby pairs with VRRP, so a failed device does not take a site offline.
VPN
IPsec IKEv2 with hybrid ML-KEM, WireGuard, OpenVPN, L2TP, GRE and VXLAN, plus remote-user VPN and out-of-band management.
Security
Zone firewall and security policies; InstaShield IP and DNS, DDoS protection, DPI, IPS, antivirus, anti-spam, web filter, app control and SSL inspection.
4G and 5G cellular
LTE Cat 4/6 and 5G SA/NSA (sub-6 GHz) by model, with APN auto-provisioning and per-SIM signal telemetry.
Industrial protocols
Modbus RTU/TCP, DNP3, IEC 60870-5-101/104, MQTT and RS232/RS485 serial for field and plant sites.
Management and reports
Web UI, NXP-CLI command line, SNMP, TR-069 and TACACS+ sign-in, with traffic, security and event reports; managed from the Nexapp Controller.
The interface your team works in
Every NexappOS device has a full web interface and the NXP-CLI command line, and joins the Nexapp Controller for fleet-wide management. These are real screens from an Enterprise X Series edge.
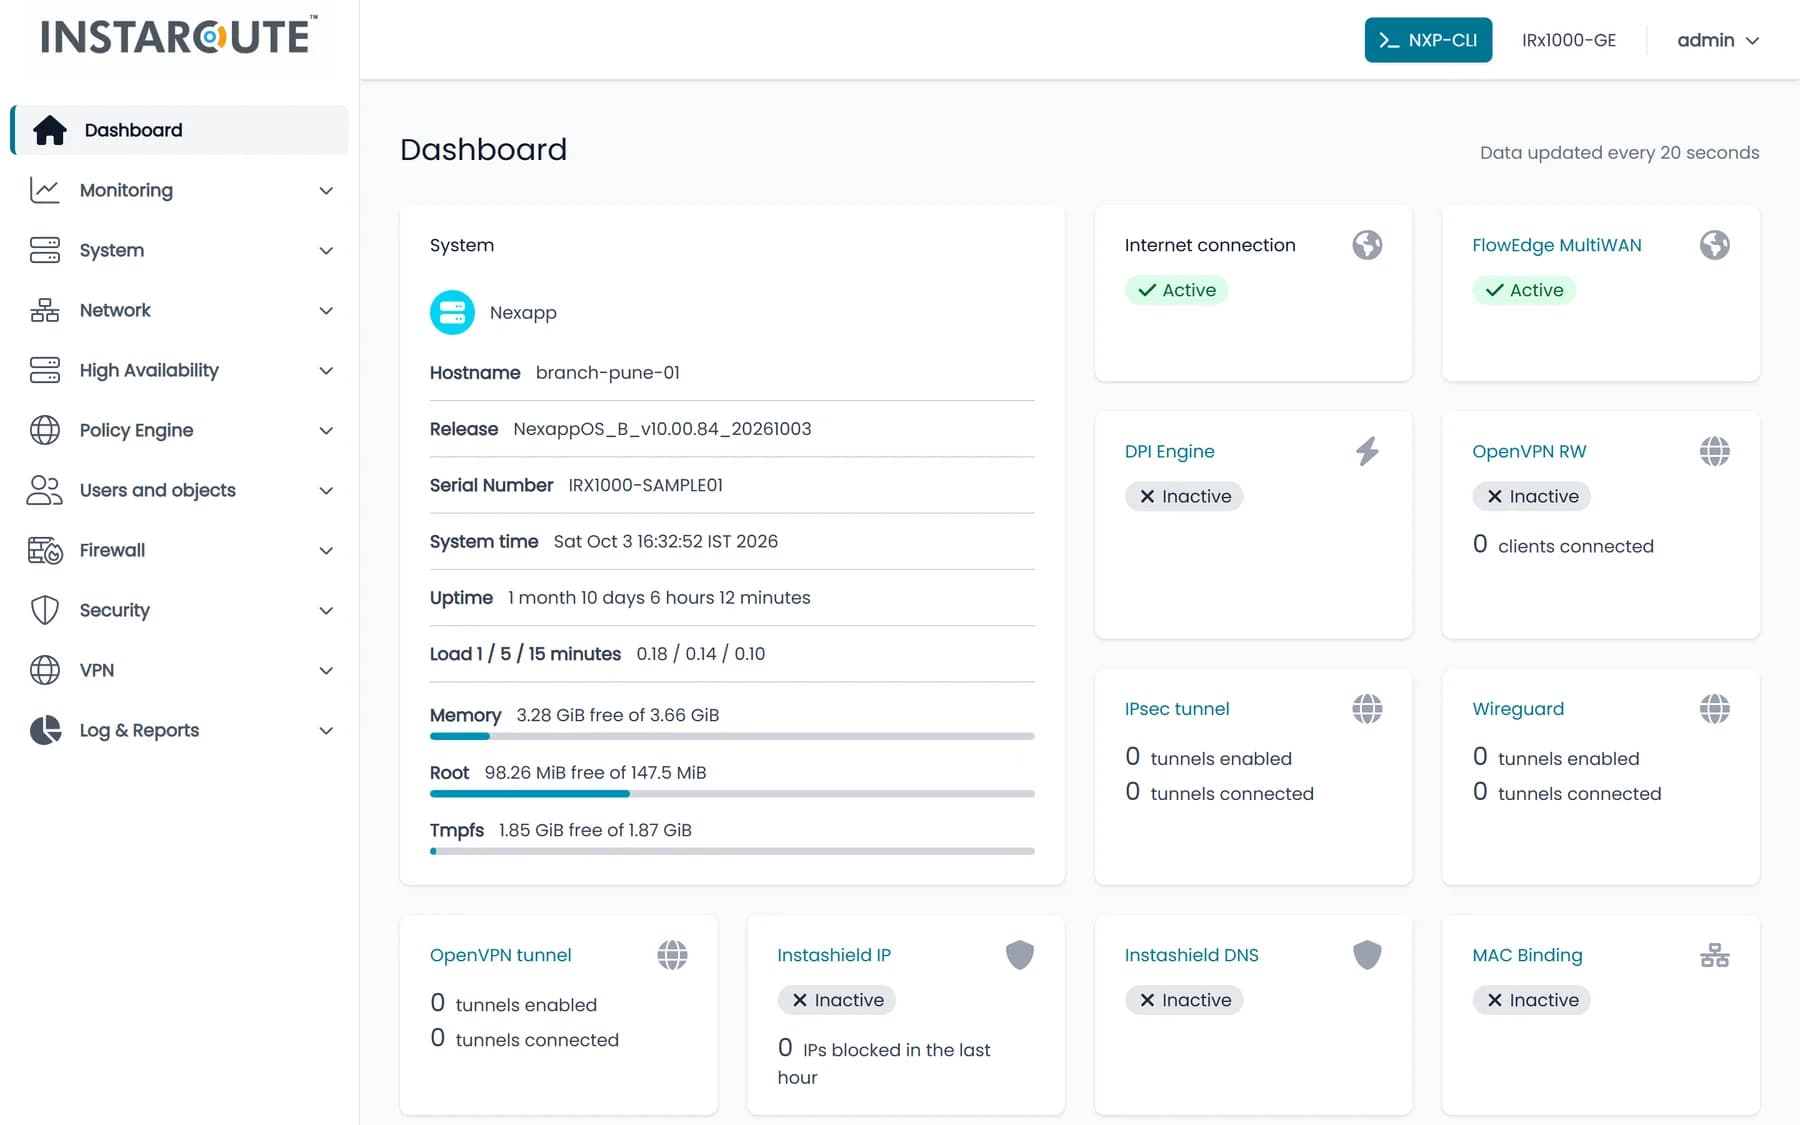
Release, uptime, load and memory, with live status for internet, FlowEdge MultiWAN, DPI, VPN tunnels and InstaShield. Real NexappOS interface, shown with sample data.
One operating system, wherever your network runs
The same NexappOS runs on hardware, in virtual machines, in public cloud and in your data centre. Features, post-quantum encryption and policy stay identical, and one console manages them all.
Same features · same post-quantum encryption · one consoleBare metal
Ships on every Instaroute router and Nexapp SD-WAN edge, and installs on standard x86 servers for high-throughput hubs.
Virtualized platforms
Runs as a virtual machine on KVM, Microsoft Hyper-V and VirtualBox, so a branch server or private cloud hosts the edge with no extra hardware.
 Hyper-V
 VirtualBox
Public cloud
Deploys as a virtual edge in AWS, Azure and Google Cloud, bringing cloud workloads into the same encrypted WAN as your sites.

 Azure

Data centres
Runs as the hub in your data centre and DR site, terminating branch tunnels with high availability.
Signed, verified, rolled out in stages
A tampered firmware image is one of the few ways to take over a network device completely. NexappOS closes that door. Staged rollout keeps a bad update from reaching your whole fleet.
- Step 1Signed at Nexapp
Every image and configuration carries a post-quantum signature.
- Step 2Verified on device
Your router checks the signature before it installs anything.
- Step 3Canary rollout
You push to a small group first, then progressively to the fleet.
- Step 4Rollback
Snapshots, diff and rollback return you to a known-good state.
You manage updates from the Nexapp Controller or Instaroute SDWAN Lite 2.0.
The full post-quantum stack, built into the operating system
Hybrid post-quantum key exchange protects your traffic recorded today against decryption later. NexappOS brings post-quantum encryption and signatures to every router, not just your data centre.
Hybrid classical + ML-KEM (NIST FIPS 203) on IPsec IKEv2 tunnels.
Post-quantum certificates (FIPS 204) for peer authentication.
X25519MLKEM768 protects device-to-controller management traffic.
You change algorithms by policy as standards evolve, without new hardware.
Every Instaroute router and Nexapp SD-WAN edge
Same firmware across the Instaroute Lite Series and the Enterprise X Series, so one skill set covers your whole estate.
Instaroute Lite Series
Instaroute 4G routers for ATMs, branches, stores and IoT/M2M sites, managed at scale from Instaroute SDWAN Lite 2.0.
Enterprise X Series
SD-WAN Enterprise edges managed from the Nexapp Controller, from the IRX100 5G edge to the IRX5000.
Transparency: SBOM and CBOM
Your auditors get a cryptographic bill of materials (CBOM). It lists the algorithms, keys and protocols NexappOS uses, in line with CERT-In's July 2025 guidelines on SBOM, CBOM and QBOM.
Request the CBOMLifecycle and support
- 24×7 NOC in Pune; one SLA across hardware, firmware and platform
- TEC MTCTE, IEC 62443, CE and RoHS at product level
Grow without changing platforms
Start with one Instaroute router on Instaroute SDWAN Lite 2.0, then add SD-WAN Enterprise, NGFW and SSE. Your firmware underneath stays the same.
See the growth pathFrequently asked questions
What is NexappOS?
NexappOS is the operating system on Nexapp devices, including Instaroute routers and SD-WAN edges, and it also runs on x86 servers, virtual machines, public cloud and data-centre hubs.
It gives you routing, VPN, firewalling, cellular management and industrial protocols. We develop and maintain it.
Can NexappOS run in the cloud or on our own servers?
Yes. NexappOS runs on bare metal, as a virtual machine on KVM, Microsoft Hyper-V or VirtualBox, as a virtual edge in AWS, Azure and Google Cloud, and as the hub in your data centre.
Every form factor has the same features, post-quantum encryption and policy, managed from one console.
How are NexappOS updates signed and delivered?
Firmware and configuration carry post-quantum signatures, and each device verifies the signature before installing.
You push updates over the air. Use a mass upgrade from the Nexapp Controller, or a canary rollout with rollback from Instaroute SDWAN Lite 2.0.
Is NexappOS post-quantum?
Yes. You get hybrid ML-KEM key exchange on IKEv2 tunnels, ML-DSA authentication, post-quantum-signed firmware and post-quantum TLS 1.3 for management.
Post-quantum mode is on by default.
Which IPsec parameters does NexappOS support?
NexappOS supports IPsec IKEv1 and IKEv2 with AES-GCM encryption, SHA-2 hashing and DH groups 14–16.
It adds hybrid post-quantum key exchange on IKEv2 tunnels.
Can I get an SBOM or CBOM?
You can get a CBOM, in line with CERT-In's July 2025 guidelines.
How long is NexappOS supported on a device?
End-of-life policy: coming soon.
See NexappOS on an Instaroute router, or get the firmware security note for your review.
24×7 NOC in Pune · 75,000+ devices deployed · 400+ enterprise and banking customers since 2014.